Case studies · AppsTek Corp
A secure, highly available EC2 container platform for AppsTek's enterprise workloads
AppsTek runs containerized workloads on EC2 across two Availability Zones with encrypted storage, automated backups and centralized logging and alerts.
- Client
- Industry
- IT services and consulting
- Location
- Addison, Texas, United States
- Engagement
- Managed services
What Cypik delivered
- Containerized application workloads on EC2 in private subnets, behind NGINX load balancing, across two Availability Zones
- Amazon RDS for MySQL as the managed database
- A GitLab Runner and Amazon ECR delivery path, with credentials held in AWS Secrets Manager
- Encryption, least-privilege IAM and automated backups with AWS Backup and EBS snapshots
- CloudWatch logs and alerts with retention policies, plus GuardDuty, AWS Config, CloudTrail and VPC Flow Logs
Results in brief
- Application servers sit in private subnets and are reached only through NGINX in public subnets
- Two Availability Zones remove a single point of failure for the web and application tiers
- Data encrypted at rest (EBS, S3) and in transit (HTTPS), with least-privilege IAM
- Automated backups with AWS Backup and EBS snapshots for fast recovery
- Centralized logging and alerts for faster incident detection and resolution
The client
About AppsTek Corp
AppsTek Corp is an AI-focused digital engineering and technology consulting company that helps enterprises modernize applications, automate business processes and improve operational efficiency. Its services include enterprise AI, application development and modernization, cloud solutions, data engineering, systems integration, quality engineering and managed services.
With expertise across platforms such as Oracle, SAP, Microsoft, NetSuite and Snowflake, AppsTek supports organizations in financial services, mortgage, manufacturing, retail, and oil and gas.
Challenge
An enterprise platform that could not afford downtime or data loss
AppsTek's enterprise customers rely on its applications and digital engineering workloads, so an outage, breach or lost dataset lands on AppsTek's own service commitments.
AppsTek needed a secure, scalable and highly available environment on Amazon EC2 for its enterprise applications. It had to perform reliably, stay responsive as workloads grew and absorb changes in demand.
- 01
Downtime risk. high availability and minimal downtime were essential to keep service continuous for enterprise customers.
- 02
Exposure. the environment needed network isolation, encryption of data at rest and in transit, strict access control and protection against unauthorized access.
- 03
Data loss risk. application data had to be safeguarded against infrastructure failures, cyber incidents and accidental deletion, with automated backups and tested recovery procedures.
- 04
Operational overhead. the goal was to simplify infrastructure management and keep operational effort low while leaving room for growth.
Solution
What Cypik delivered
Architecture
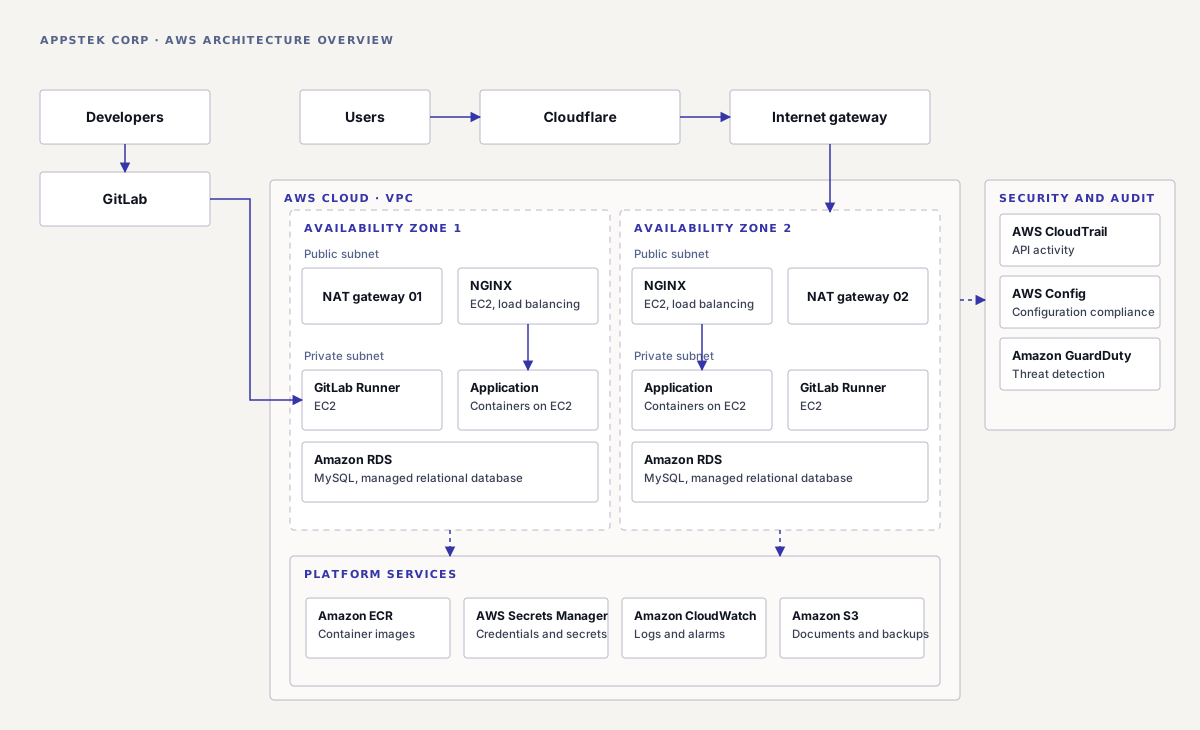
- We designed containerized workloads on Amazon EC2 instances. Containers give portability, scalability and consistent environments across development and production.
- Application containers and their GitLab Runner instances run in private subnets of a VPC that spans two Availability Zones. Security groups and network ACLs control inbound and outbound access.
- NGINX on EC2 in the public subnets load balances traffic to the application containers, behind Cloudflare and an internet gateway. NAT gateways in each zone give the private subnets controlled outbound access.
- Amazon RDS for MySQL is the managed relational database for application data.
Delivery
- Developers push code to GitLab, and GitLab Runner runs the CI jobs, and Amazon ECR stores container images securely.
- AWS Secrets Manager holds credentials and secrets, so they stay out of code and images.
Security
- IAM roles follow least-privilege access, EBS volumes are encrypted, and traffic uses HTTPS.
- Application documents and backups are stored in Amazon S3 with encryption enabled.
- Amazon GuardDuty, AWS Config, AWS CloudTrail and VPC Flow Logs provide threat detection, configuration compliance, API audit and network visibility.
Operations and recovery
- Amazon CloudWatch collects application and system logs in real time, with retention policies and alerts that flag anomalies early.
- AWS Backup and EBS snapshots protect data on a schedule and support fast recovery.
Architecture
How it is built.
Select a diagram to open it at full size.
Outcome
A resilient, observable foundation for growth
The environment gives AppsTek a secure, scalable and highly available platform for its enterprise workloads, with a footing to take on more.
- 01
Running across two Availability Zones, with application servers in private subnets behind NGINX, removes a single point of failure and keeps the application tier off the public internet.
- 02
Containerization makes development and production consistent and simplifies application management, while EC2 keeps flexibility and performance.
- 03
Centralized logging and alerts in Amazon CloudWatch improved operational visibility and enabled faster incident detection and resolution.
- 04
Encrypted EBS volumes and S3 storage, strict IAM controls and continuous monitoring strengthened the security posture.
- 05
Automated backups with AWS Backup and EBS snapshots protect application data and support rapid recovery.
Security
How the environment is secured
Network isolation, encryption, least-privilege access and continuous monitoring work together to protect application data.
Network isolation
- Application containers and GitLab Runner instances run in private subnets.
- Security groups and network ACLs control inbound and outbound access.
- Only NGINX and the NAT gateways sit in public subnets.
Identity and secrets
- IAM roles apply least-privilege access.
- AWS Secrets Manager stores credentials and secrets, with rotation.
Encryption
- EBS volumes and Amazon S3 storage are encrypted at rest.
- Communication uses HTTPS in transit.
Monitoring and audit
- Amazon CloudWatch collects logs and alerts, with retention policies applied.
- AWS CloudTrail and VPC Flow Logs record API activity and network traffic.
- Amazon GuardDuty detects threats, and AWS Config tracks configuration compliance.
Backup and recovery
- AWS Backup runs scheduled backups, and EBS snapshots add volume-level protection.
Services and technology
What the environment runs on.
Compute and containers
- Amazon EC2Application containers
- Amazon Elastic Container RegistrySecure container image storage and management
Networking
- Amazon VPCTwo Availability Zones with public and private subnets
- Internet gateway and NAT gateways
- Security groups and network ACLsInbound and outbound access control
Data and storage
- Amazon RDS for MySQLManaged relational database for application data
- Amazon S3Encrypted storage for application documents and backups
- Amazon EBSEncrypted volumes with snapshots
Security and audit
- AWS Secrets ManagerSecure storage and rotation of credentials and secrets
- AWS IAMRoles with least-privilege access
- Amazon GuardDutyContinuous threat detection and security monitoring
- AWS ConfigContinuous configuration monitoring and compliance tracking
- AWS CloudTrail and VPC Flow LogsAPI activity and network traffic monitoring
Operations and recovery
- Amazon CloudWatchCentralized logs
- AWS BackupAutomated and scheduled backups
Other technology
- CloudflareEdge in front of the internet gateway
- NGINXLoad balancing on EC2 in the public subnets
- GitLab and GitLab RunnerSource control and CI jobs
More case studies
Related work.
Want results like these in your environment?
Start with a read-only assessment. You keep the written findings either way.